Employing Fusion of Neural Networks and Machine Learning Models in SQL Injection Attack Detections
Article Sidebar
Main Article Content
Abstract
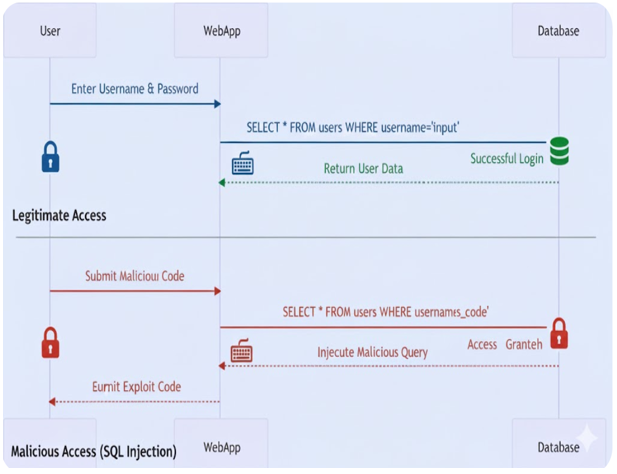
SQL injection attacks are among the most serious threats to web application security. Their main purpose is to have unauthorized access to sensitive information by exploiting related vulnerabilities. This paper proposes a multi-model approach in the detection of SQLIA by leveraging several machine learning algorithms, including Convolutional Neural Networks, Logistic Regression, Random Forest, Support Vector Machines, Naive Bayes, and Decision Trees. The focus of this work is to utilize the strengths of these models in analyzing the structure and semantics of SQL queries to distinguish between malicious and benign inputs. The paper outlines a comprehensive methodology, including data preprocessing, feature extraction, model training, and performance evaluation. Using two datasets: the first dataset containing 3951 SQL queries and the second containing 33,726 queries. The accuracy results from the small dataset were 96% for CNN, and 96.7% for Naive Bayes. On the large dataset, accuracy increased to 97% for CNN, and 98% for Naive Bayes. A fusion of Logistic Regression, Random Forest, and SVM, which resulted in 98% accuracy on the small dataset. These findings suggest that deep learning techniques, especially CNNs, along with other machine learning models and fusion techniques, hold much promise for enhancing web application security by providing a robust and adaptive solution to mitigate the risks posed by SQL injection attacks.
Downloads
Article Details

This work is licensed under a Creative Commons Attribution 4.0 International License.
How to Cite