Machine Learning–Driven Intrusion Detection System for Industrial IoT Networks Using Cross-Layer Features
Article Sidebar
Main Article Content
Abstract
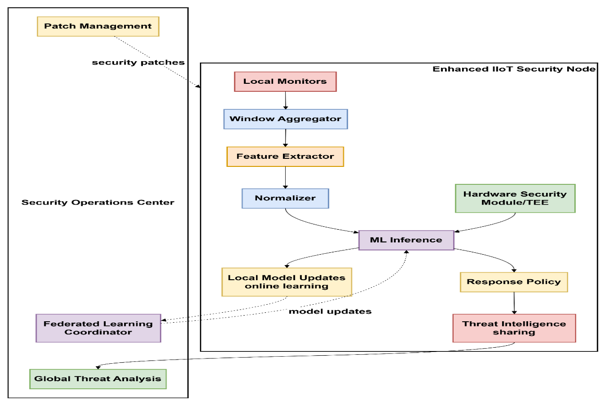
Industrial Internet of Things (IIoT) networks increasingly rely on low-power wireless stacks (e.g., IEEE 802.15.4/TSCH, 6LoWPAN, RPL) to connect sensors, actuators, and gateways in safety- and mission-critical environments. These networks remain vulnerable to multi-layer attacks such as control-plane manipulation (e.g., RPL rank/version attacks), resource depletion (e.g., flooding), and selective forwarding. Many existing intrusion detection systems (IDS) observe only a single layer, which can lead to high false positives under interference, load variations, and topology changes. This paper proposes a machine learning–driven IDS that uses cross-layer features spanning PHY, MAC, network, and transport/application indicators. The proposed system builds per-node, per-window feature vectors that capture both direct anomalies (e.g., sudden DIO spikes) and cross-layer inconsistencies (e.g., high retransmissions with stable link quality). We present a complete design: feature model, windowing and labeling strategy, training pipeline with scenario-wise splits to reduce leakage, lightweight online inference for constrained devices, and an evaluation protocol over diverse network conditions. We provide reproducible pseudocode and reference implementation guidance. Experimental results should be reported using F1, PR-AUC, ROC-AUC, false-positive rate per hour, detection latency, and energy/CPU overhead. Placeholders are included for measured outcomes and tables/figures.
Downloads
Article Details

This work is licensed under a Creative Commons Attribution 4.0 International License.
How to Cite